

Towards Secure AI Systems
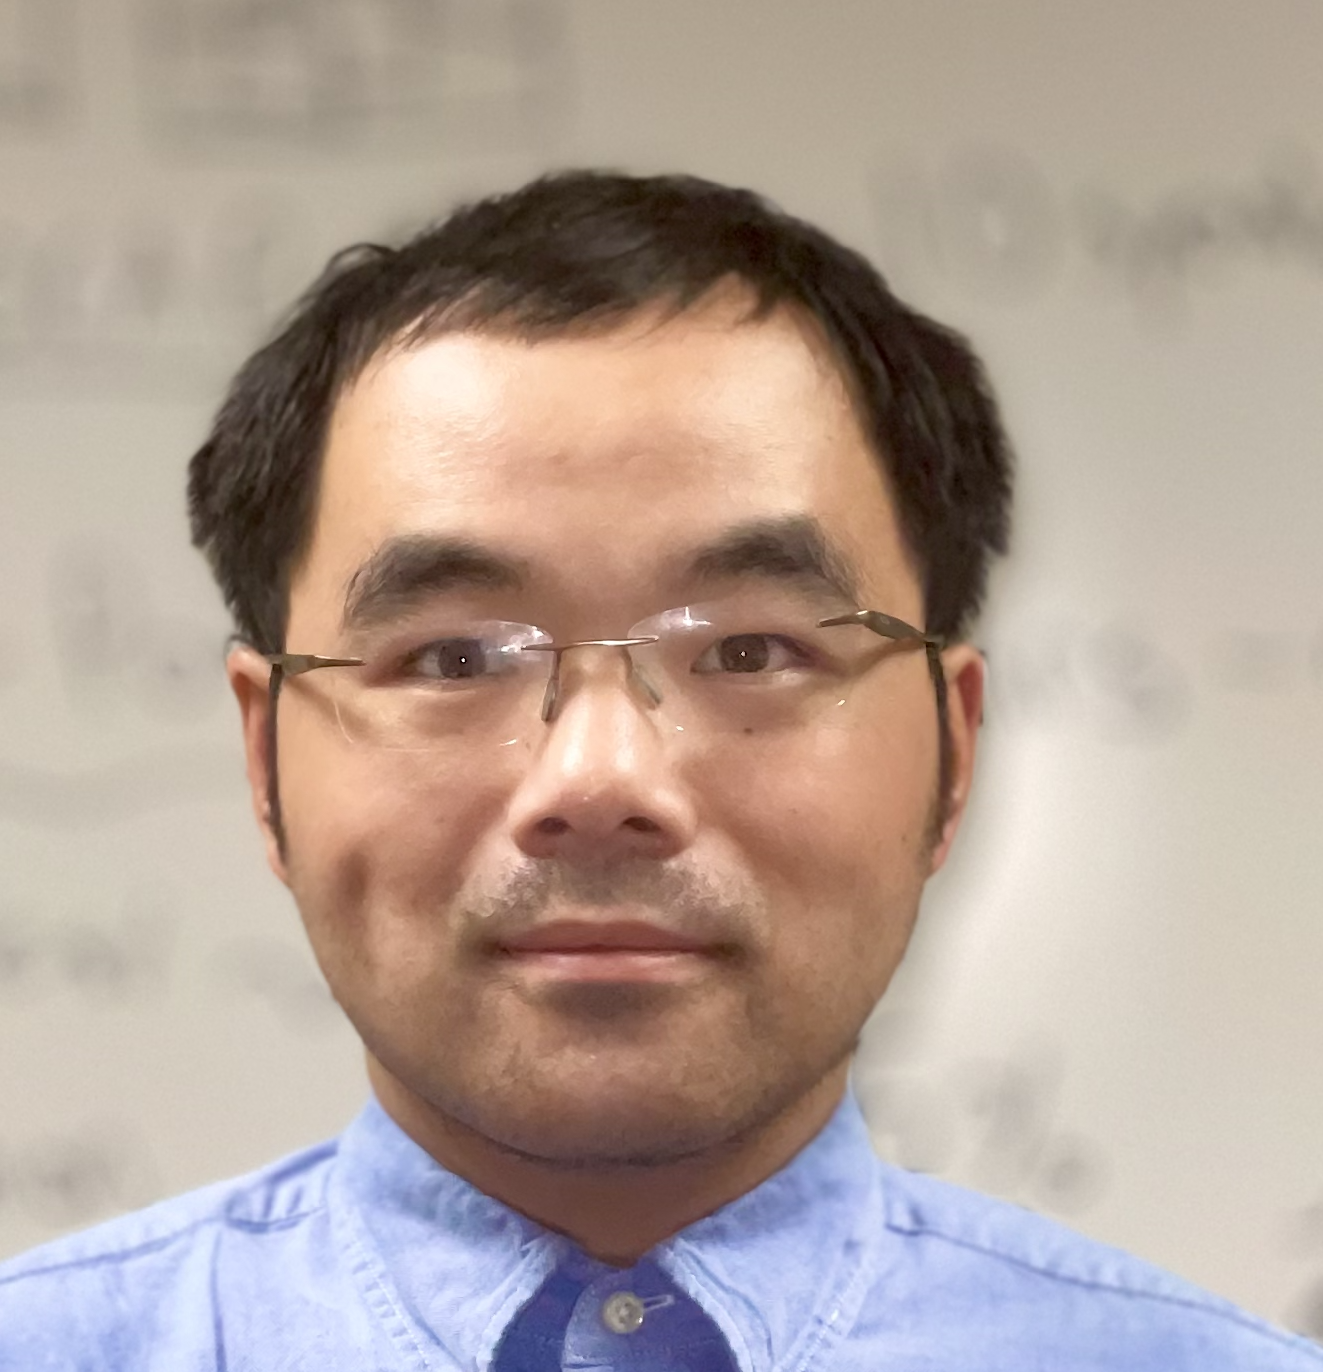
Mulong Luo · Computer Science Colloquium Series
| Speaker | Mulong Luo |
| Date | Friday, November 6, 2:15 – 3:05 pm |
| Location | 307 Love |
Abstract
How can we harness AI to uncover security weaknesses while ensuring that AI systems themselves remain secure, efficient, and accountable? This talk explores this question through three recent research projects.
First, Mulong will discuss how reinforcement learning can help discover processor vulnerabilities by searching for subtle interactions that are difficult to identify through manual analysis. Next, the talk will examine AI-based authorship attribution, illustrating how the ability to infer an author’s identity creates new challenges for privacy and anonymity. Turning to AI systems themselves, Mulong will present OverServe attacks, showing how coordinated manipulation of prompts and tools can drive excessive resource consumption in agentic AI systems.
Together, these projects highlight the dual role of AI as both a tool for security analysis and a system requiring protection.
About the speaker
Mulong Luo’s research spans the broad areas of computer security, computer systems, AI for security, and AI security. In particular, Mulong is interested in how modern AI techniques—such as large language models (LLMs) and reinforcement learning—can help build more secure computer systems, as well as how computer systems should be designed to provide stronger safety assurances for AI.